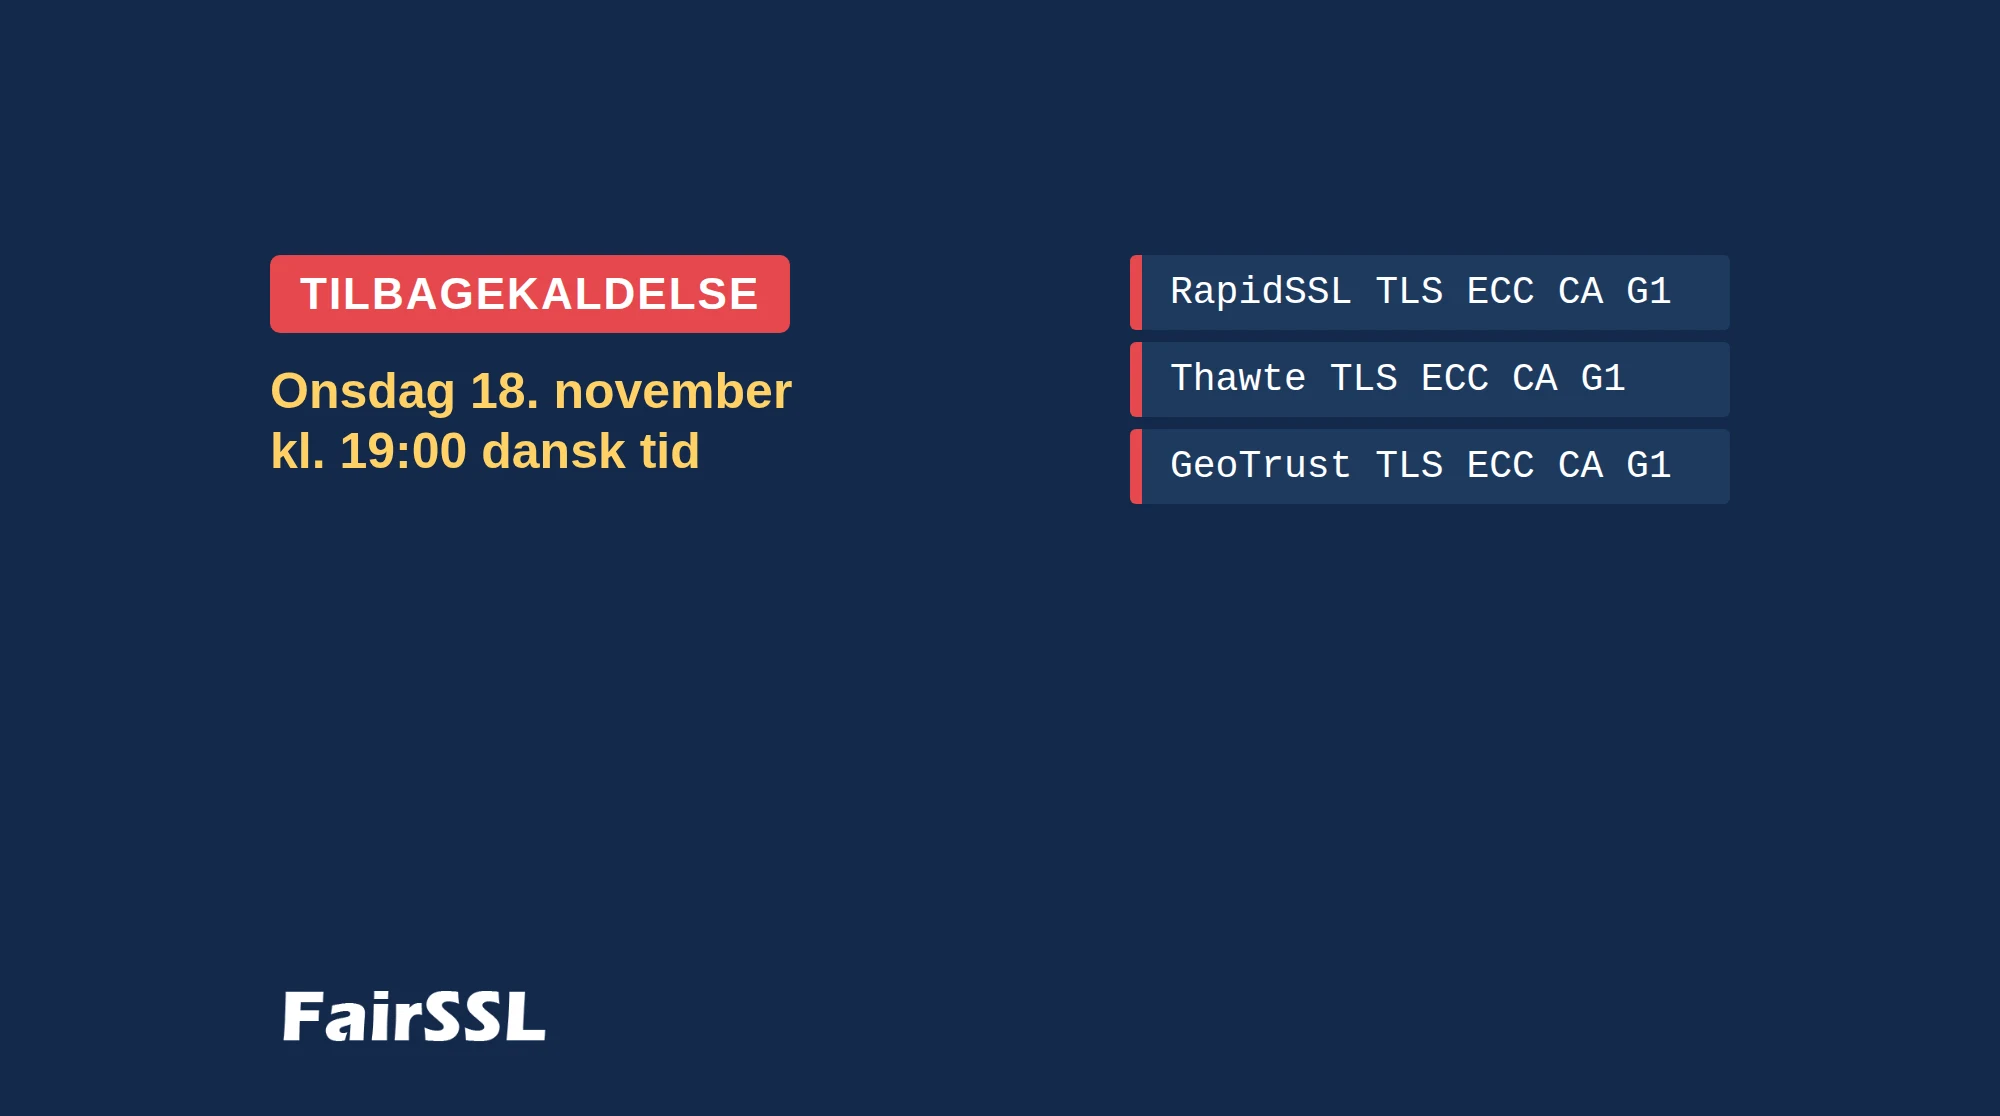
DigiCert has found an error and closes three ECC intermediate certificates under the root certificate DigiCert Global Root G3 on Wednesday 18 November 2026 at 19:00 CET (Copenhagen time, 18:00 UTC). Every certificate issued from them is revoked at the same time.
If your certificate is issued by one of these intermediates, it must be reissued and installed before Wednesday. Reissuing is free.
RapidSSL TLS ECC CA G1Thawte TLS ECC CA G1GeoTrust TLS ECC CA G1
If a different issuer is shown on your certificate, it is not affected.
What is the error?
The root certificate DigiCert Global Root G3 has an ECC P-384 key. The rules require a P-384 key to sign with SHA-384, but the three intermediates were signed with SHA-256 in 2017. The encryption is not weakened and no keys are compromised. The intermediates simply do not follow the rules and are therefore closed.
How to check your certificate
- With our SSL Scanner: enter the domain in the SSL Scanner. If the certificate is affected, the scanner shows a red warning at the top.
- In the browser: click the icon to the left of the address, view the certificate and see who is shown as the issuer.
- From the command line:
openssl s_client -connect www.example.com:443 -servername www.example.com </dev/null | openssl x509 -noout -issuer
What to do
- Order with FairSSL: create a new CSR, reissue for free in the control panel and install the new certificate before Wednesday at 19:00 CET.
- FairSSL ACME with an ARI client: servers with ACME clients that support ACME Renewal Information (ARI) are told automatically to reissue and install a new certificate. This covers, for example, Simple-Acme, win-acme 2.2.9+, lego, Certbot 4.1+, Posh-ACME, Caddy and acme.sh 3.1.4+.
- FairSSL ACME without ARI: the client waits for its next scheduled renewal, so force a renewal now.
- Your own DigiCert CertCentral account: reissue in CertCentral.
- Bought elsewhere: contact the company you bought the certificate from.
Which issuer does the new certificate get?
DigiCert has created three new intermediates under G3, signed with SHA-384:
RapidSSL G3 TLS ECC P-384 SHA384 2026 CA1Thawte G3 TLS ECC P-384 SHA384 2026 CA 1GeoTrust G3 TLS ECC P-384 SHA384 2026 CA1
Until the new intermediates issue, we issue ECC certificates from RapidSSL, Thawte and GeoTrust from the intermediate under the root certificate DigiCert Global Root G2 (RSA). The certificate keeps its ECC key; only the issuer is different. We test the new G3 intermediates every hour, and as soon as they issue, we use them for ECC certificates.
DigiCert switched to the G5 root certificate as the default on 12 November 2026, but still issues from G2/G3 on request. From 8 June 2027, DigiCert no longer issues from the G2 and G3 root certificates.
What we have done
We have written directly to the customers who have or monitor an affected certificate. On every affected certificate from our ACME server we have started automatic replacement with ARI. Because ARI solves errors like this one, we recommend using only ACME clients that support ARI.
If you have questions, write to info@fairssl.dk.